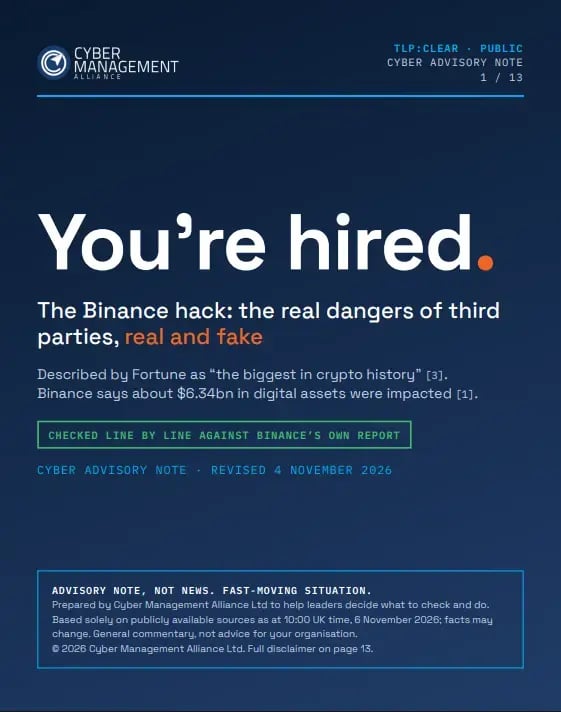
Download Our Cyber Advisory Note on the Massive Binance Cyber Attack
The October 2026 cyber attack on Binance exposed serious weaknesses in third-party security and incident containment. According to Binance's initial findings, approximately $6.34 billion in digital assets were impacted in a sophisticated attack involving compromised developer software, a fake recruitment process and the misuse of internal systems. The incident is a reminder that even organisations with established security controls can be vulnerable to attacks that unfold gradually over several months.
Cyber Management Alliance's 13-page Binance Cyber Advisory Note examines how the attack unfolded, the methods used by the attackers and the wider implications for businesses. Based on publicly available information and checked against Binance's official report, the advisory separates confirmed findings from unanswered questions. It also highlights the risks associated with third-party tools, social engineering and internal AI systems, along with the challenges of containing an attack once critical systems have been compromised.
Download the free Cyber Advisory Note for a detailed breakdown of the incident, six practical cybersecurity recommendations and five important questions every board should consider. The advisory is designed to help business leaders and security teams review their existing controls, identify potential gaps and strengthen their readiness for similar incidents.
Disclaimer: This document has been created with the sole purpose of encouraging discourse on the subject of cybersecurity and good security practices. Our intention is not to defame any company, person or legal entity. Every piece of information mentioned herein is based on reports and data freely available online. Cyber Management Alliance neither takes credit nor any responsibility for the accuracy of any source or information shared herein.
- ** GDPR ** We wholeheartedly believe your and our rights to privacy and in the GDPR. The bottom of the page explains how we use your data.
- Align with the GDPR requirements.
- Increase your Breach Readiness.
- Reduce your time to detect and respond.
Complete the form below to receive a copy of our Cyber Advisory on the Binance Hack
We are industry experienced practitioners when it comes to cyber security training & cyber security consultancy services
Training
We offer a host of courses including our NCSC Assured Training in Cyber Incident Planning and Response and our NCSC Assured Training in Building and Optimising Incident Response Playbooks.
Virtual CISO Services
Hands On, full-support 'Security As a Service', specifically designed for organisations that require access to experienced cybersecurity, governance, risk and compliance professionals.
Virtual Cyber Assistant
A unique, affordable, subscription-based, cybersecurity service for small to medium businesses, offering 280+ services in cybersecurity.
Cyber Crisis Tabletop Exercises
Scenario-based, verbally-simulated tabletop attack exercises that test your organisation's ability to effectively respond to a cyber-attack.