Date: 22 September 2026
If you look at most blogs about AI firewalls, they all say the same thing: “uses AI, more intelligent, next-gen.” That sounds appealing, but it doesn't help you decide what to buy or deploy.
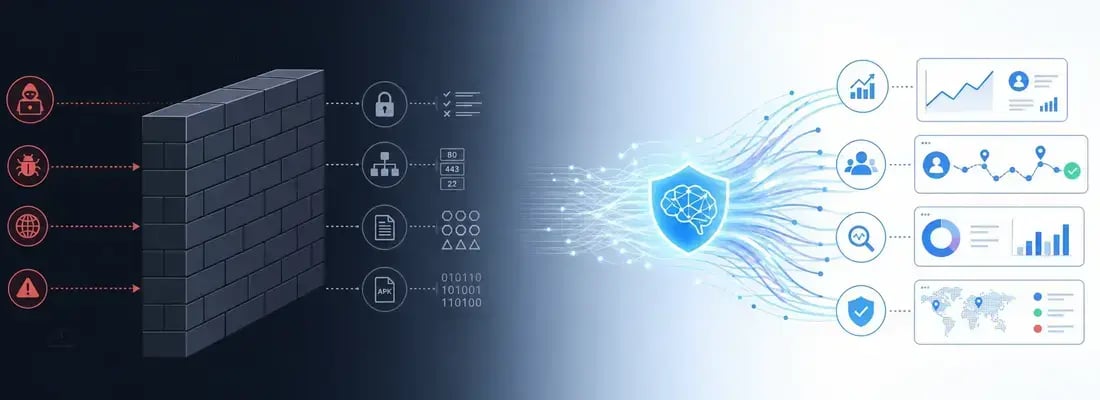
The key difference is this: traditional NGFWs filter ports, IPs, and basic app signatures, while an AI firewall focuses on user and application intent. Instead of only asking, “Is this port allowed?" it keeps asking, “Does this behavior make sense for this user, this app, right now?”
Let’s break that down in simple, practical terms.
How Traditional NGFWs Think
NGFWs were a big step forward from old stateful firewalls. They added:
- Deep packet inspection
- Application identification
- User identity mapping via directory services
- Basic intrusion prevention and URL filtering
But at their core, they still live in a rules-first world:
- You open specific ports and protocols
- You whitelist certain apps or signatures
- They also lean on firewall rules and policies to control what traffic gets through in the first place.
If traffic matches a known “good” pattern on the right port, it is allowed. If it matches a known “malicious” signature, it is blocked.
This approach works fine for north-south traffic and predictable applications. The problems start when:
- Almost everything is encrypted
- Apps move to SaaS and change frequently
- Users connect from everywhere
- Attackers use built-in tools and look normal until the last step
NGFWs can still help, but they are often blind to intent. For example, a data exfiltration over HTTPS on port 443 can look just like normal web browsing on the same port.

How an AI Firewall Thinks
An AI firewall usually sits alongside or on top of your existing controls. It still respects ports, IPs, and apps, but it has a different brain.
Instead of checking only “Does this match a rule?" it keeps learning:
- What is normal for this user, device, and service
- How this app behaves during a normal workday
- Whether a new flow matches the business intent behind the policy
Some key ideas:
- Intent-aware enforcement
Policies are written closer to business language. For example:
“Finance users can export up to a certain number of records from ERP to approved destinations during business hours.”
The AI firewall then checks whether real traffic still matches that intent.
- Behavioral baselines
It builds baselines for users, devices, apps, APIs, and service accounts.
When behavior drifts, such as a backup service starting to send data to a new region at odd hours, it can challenge, throttle, or block, even if the port and protocol look fine.
- Context-rich decisions
Instead of relying on a single rule hit, decisions can factor in user, device posture, app, data type, history, time, location, and a current risk score.
Done properly, an AI firewall does not instantly replace your NGFW. It wraps and enriches it. You still have control over ports and policies, but the system helps you enforce them in a way that tracks real-world intent, not just static rule sets.
Concrete Capability Comparison
Here is a straightforward look at how the two approaches differ in practice:
|
Capability |
Traditional NGFW |
AI Firewall |
|
Core decision model |
Port and protocol rules plus app signatures and IPS |
Intent-aware policies, behavioral models, and risk scoring |
|
Visibility into encrypted traffic |
TLS inspection, SNI, limited content awareness |
Uses patterns and metadata to infer behavior even when content is opaque |
|
User and app context |
Maps IPs to users, basic application awareness |
Deep profiles of users, devices, apps, and typical behavior |
|
Policy expression |
“Allow app X on port Y for group Z” |
“Allow business action A by role B under conditions C” |
|
Zero Trust alignment |
Can segment, mostly manual and coarse-grained |
Fine-grained, dynamic, identity and context driven |
|
Handling unknown threats |
Signature and feed based, plus basic heuristics |
Learns continuously, flags anomalies, and adapts automatically |
|
Response to abnormal behavior |
Mostly allow or block, some rate limiting |
Can challenge, add step-up auth, throttle, isolate, or auto-tune rules |
|
Fit for cloud and SaaS-heavy envs |
Works, but often blind to detailed app behavior |
Designed to understand app flows and user journeys end to end |
Why Intent-Aware Enforcement Matters Now
The reason intent-aware enforcement has become so important is simple: modern attacks hide inside “allowed” paths.
- Data theft hides in normal HTTPS sessions
- Account takeover hides in normal login flows
- Lateral movement hides in standard admin tools
This is precisely why more security teams are leaning on behavioral analytics to catch what a static rule would wave through.
A rules-driven NGFW is great at saying “No” to what you already know is bad and “Yes” to what you already defined as good. What it struggles with is all the traffic that looks fine on paper but feels wrong in context.
An AI firewall aims to live in that grey area. It can:
- Notice when a regular user suddenly behaves like an admin
- Catch a service account that starts talking to new, unusual destinations
- See that an API client is abusing an endpoint in a way that does not match typical usage, even if each request looks valid by itself
This is the practical difference that matters: it helps you catch abuse of allowed channels, not just classic blocked ones.
Should You Replace Your NGFW Right Now?
In most real networks, the short answer is no. Today, many teams end up with a combined setup:
- The traditional NGFW still handles core perimeter work: port control, basic app filtering, IPS, VPN, and audit requirements
- The AI firewall layers on top of or beside it and focuses on intent, behavior, and context, then feeds decisions back into enforcement
The broader industry conversation has shifted the same way, with more focus now on tightening identity-driven access controls rather than adding more static rules.
You can think of it like this:
- The NGFW is the gate and the guard
- The AI firewall is the detective and the investigator, always watching what people and services actually do after they pass through that gate
Over time, as models mature and teams get more comfortable with intent-based policies, more of the allow and deny logic can move into the AI-powered layer. For now, most teams will run both together.
Final Thoughts
If you are evaluating products, do not stop at “uses machine learning” in the marketing copy. Ask sharper questions:
- How does the product define and enforce intent?
- What exactly does it baseline and learn over time?
- How does it behave when something is suspicious but not clearly malicious?
- How well does it work with your existing NGFW stack?
The goal is not to buy buzzwords. The goal is to move from a world of fixed, port-based rules to a model where your AI firewall understands what your users and apps are supposed to do and has the intelligence to step in when real behavior stops matching that intent.