Hero Background
Cyber incident planning and response training

CIPR-AI: Cyber Incident Planning & Response Course for the AI Era

Practise the decisions that shape your cyber incident response.

CIPR-AI combines incident response planning with practical exercises in managing AI, ransomware and third-party incidents. Build the skills to coordinate your response, brief senior leaders and assess reporting obligations.

Explore the curriculum below, or view the live virtual classroom dates.

NCSC Assured Cyber Incident Planning and Response Training Course & Certification
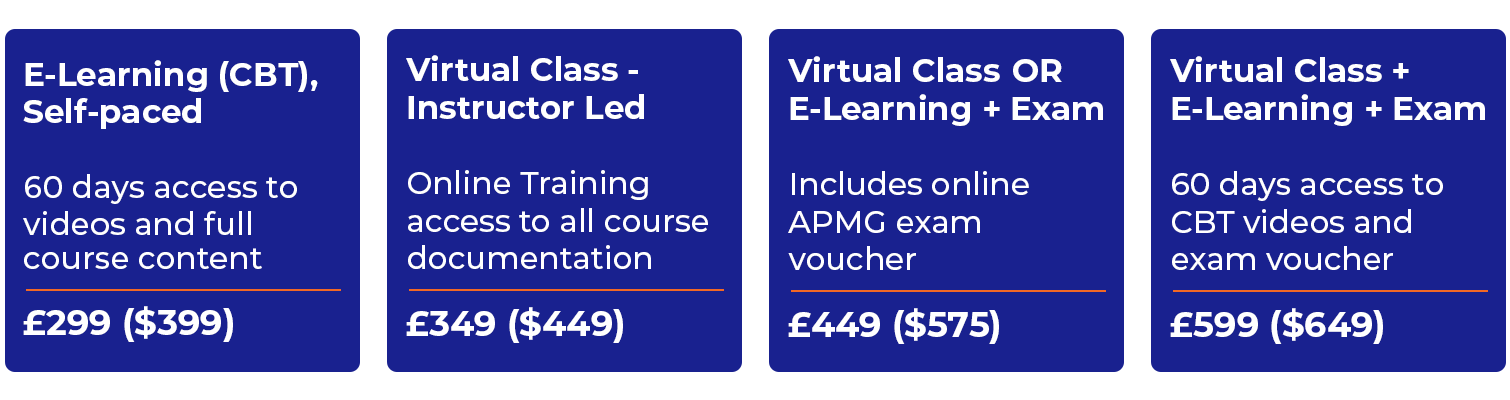
CIPR Web Page 4 boxes image

CIPR OFFER BANNER CTA

Self-Paced eLearning

Online Immediate Access

Access self-paced eLearning

Virtual Live Class

Wednesday 28th October & Thursday 29th October

View live course dates

Virtual Live Class

Wednesday 18th November & Thursday 19th November

View live course dates


Certified cybersecurity training course that teaches you how to: 

  • Implement NIST's Incident Response Framework
  • Meet all the objectives of ISO 27001:2022 Annex A (A.5.24–A.5.28)
  • Reduce your time to detect and respond to cyber-attacks

The NCSC Assured Cyber Incident Planning & Response Course (CIPR) is a comprehensive training enabling you and your team to prepare a well-defined and managed approach to handling a data breach or a cyber-attack. Created by Cyber Management Alliance, the leading global experts in cybersecurity training and advisory services, this cyber incident response certification and course has helped several clients globally enhance their cyber resilience. 

The course is aimed at a wide audience, both technical or non-technical, who want to understand how to better prepare for responding to a cyber-attack. The course has no pre-requisites and students will understand the operational strategies and processes an organisation needs to consider before, during and after a cyber crisis or data breach. 

Day 2 of this course is especially valuable for CISOs, incident managers, SOC leads, and risk, compliance, legal and DPO professionals, as well as internal and external auditors who must evidence how incidents are decided, reported and closed.

New CIPR-AI: Incident Response Training for the AI Era

  1. Respond at the speed of the threat. On average, an attacker spreads from the first system they break into to other systems within 48 minutes; the fastest do it in under a minute (CrowdStrike 2025 Global Threat Report). Under EU rules such as DORA and NIS2, your first report to a regulator can be due within 4 to 24 hours. Practise both.
  2. Built on NIST's 2025 guidance. Learn incident response as NIST now frames it: part of governance and risk management, not a technical afterthought.
  3. Train, don't just listen. Every new module ends in a live exercise that leaves you with a record of your decisions, a checklist or a draft notification to a regulator you can use at work the next day.

What's new

  • Aligned throughout to NIST SP 800-61 Rev 3 and the NIST Cybersecurity Framework 2.0
  • Three new modules open Day 2, in this order: AI Incident Response; Ransomware Incident Response; Identity, SaaS and Third-Party Incidents (stolen logins, cloud apps and suppliers)
  • Day 2 now covers UK, EU and Swiss reporting deadlines side by side
  • Every existing module refreshed with 2026 content

What happens on which day

  • Day 1: the NCSC Assured core (Modules 1–11).
  • Day 2 (optional): AI Incident Response first, Ransomware Incident Response second, and Identity, SaaS and Third-Party Incidents third, followed by Regulated Incident Response and real-incident case studies. 

NCSC assurance and examination

Day 1 Modules 1–11 form the NCSC Assured core and are covered by the optional APMG International examination.

The new Day 2 modules, regulated incident response content and “New for 2026” additions are Cyber Management Alliance additions. They are not included in the NCSC assurance or the optional examination.

The new modules are taught live, in the virtual classroom and in-house. Past CIPR delegates can book Day 2 only without repeating Day 1: see "Past CIPR delegates: upgrade to CIPR-AI" below.

Highlights of the Online, Live & Public CIPR Training

Training assured by the UK-Government's National Cyber Security Centre (NCSC)

Teaches how to implement NIST's Computer Security Incident Handling Guide: NIST SP 800-61 Revision 3

Enables meeting the objectives of ISO 27001:2022 controls 5.24–5.28.

Accredited by the Chartered Institute of Information Security (CIISec)

Optional Examination (Provided by APMG International and ProctorU)

Interactive exercises covering incident planning, response and recovery

Bonus content including worksheets and templates

Access to several accompanying mind-maps and checklists

Full access to all content (downloadable PDFs) for 60 calendar days (E-Learning students only)

Comprehensive supporting e-book for reinforced learning

Access to regular live-discussions with global experts (online students only)

Exclusive group remote and onsite workshops available

Benefits of this NCSC Assured Training

Why do you need the Cyber Incident Planning & Response Training?

This NCSC Assured Training on cyber incident response planning teaches you the best practices and proven strategies.
 
It provides senior management and incident response teams, amongst others, with the vital knowledge and skills to plan, lead and manage a cyber crisis. It equips learners with competence so that they can rapidly detect, respond to and recover from a cyber crisis.Strong cyber incident response planning equips senior management and response teams to plan, lead and manage a cyber crisis.
 

Choose your attendance option

  • Day 1: The NCSC Assured core, covering Modules 1–11.
  • Full two-day programme: Day 1 plus the new AI, ransomware and identity/SaaS/third-party modules, regulated incident response and practical exercises on Day 2.
  • Day 2 only for existing clients and past CIPR delegates: Attend Modules 12–15 and their submodules without repeating Day 1. There is no half-day option.

Day 2 is currently available only through live training, not self-paced eLearning. Live virtual classroom and private organisational training options are available.

Directly download the complete Learning Objectives PDF


Gain a deep understanding of NIST's Computer Security Incident Handling Guide: NIST SP 800-61 Revision 3.

Get insights on the latest techniques and core principles of effective cyber incident response.

Learn how Threat Intelligence-led testing works & what response frameworks are adopted by leading governments & institutions.

Gain mastery over the Cyber Kill Chain and understand how to design an early warning system to lower discovery time from months to days

Attain familiarity with the core concepts of incident triage, OODA and their relevance & importance in a cyber resilient organisation

Become proficient with the primary requirements of privacy regulations, like the EU-GDPR and DORA, in the context of cyber incident response

Prepare for modern cyber incidents

Your incident response plan needs to account for AI-assisted fraud, compromised identities, cloud applications and incidents at suppliers. Practise how your organisation will make containment and recovery decisions, coordinate stakeholders and assess which reporting obligations apply.


Practise decisions before a real incident

Use CIPR-AI’s live exercises to rehearse the decisions your organisation will face during an incident:

  • Verify a suspected deepfake payment request through a separate, trusted channel.
  • Decide who can switch off an AI agent and what business activity will be affected.
  • Set recovery priorities and assess the legal, insurance and sanctions considerations of a ransom decision.
  • Coordinate a supplier incident, record your decisions and assess customer and regulator notification requirements.

Explore the Day 2 syllabus for the exercises and practical takeaways.

The speed and sophistication of phishing campaigns has increased rapidly with  AI-assisted attacks

Backups, identity systems and recovery infrastructure are now top targets, making rapid cyber incident response essential 

Ransomware groups are targeting supply chains and critical infrastructure

Cloud and SaaS breaches are becoming a major incident response challenge

Regulators now expect organisations to regularly test cyber resilience capabilities

Cyber insurers are now assessing incident response maturity before issuing coverage

Benefits of the NCSC Assured Incident Response Training

There are numerous individual advantages of learning about cyber incident response plans, incident response certifications and knowing how to enhance your incident response capabilities and breach response maturity.

We also run an internal private workshop for organisations who wish to enhance their cyber resilience through improved and a more coordinated response to cyber-attacks. Organisations who invest in the NCSC Assured Cyber Incident Response Training Course for their staff observe a great degree of improvement in their cybersecurity maturity and cyber resilience.

The table below lists the benefits to both individuals and organisations who undergo our NCSC Assured Training.  

Individual Benefits

Organisational Benefits

Gain a deep understanding of NIST's Computer Security Incident Handling Guide: NIST SP 800-61 Revision 3. Learn how to implement NIST's Cyber Incident Response Framework throughout your organisation.
Become Certified in Cyber Incident Planning and Response.  Define the threat actors and create a threat actor library specific to your organisation. Define Normal - understand your organisation's baseline.
Display your incident response certifications or accreditation via a digital badge, showcase to potential clients and employers. Assess and improve your organisation's triage capabilities. Define and improve alerts for your analysts.
Comprehend and manage the threats and risks relating to information systems and assets from cyber-attacks. Become more compliant with data breach response regulations by creating fit-for-purpose data breach response plans.
Define and support the implementation of processes and procedures for detecting breaches of security policies.  Achieve tangible reductions in detection and response times to cyber-attacks that could lead to better managed and lower data breach compensations.

Understand the core principles of and actively contribute to the creation of your organisation’s cybersecurity strategy and incident response plans.  Streamline technology investments with the possibility of tangible savings across multiple technology sets.
Explain what Threat Intelligence and its significance is in keeping organisations cyber-resilient. Discuss how Threat Intel can aid in rapid detection of advanced threats. Create organisation specific cyber-attack scenarios.
Participate in the development of information risk management strategies to reduce business risk. Build Detection & Response Strategies tailored to your business. 
Discuss the benefits of monitoring and auditing for violations of relevant security policies (e.g. acceptable use, security, etc.). Technology stack review & assessment of integration into SoC & monitoring technologies. High level review of your monitoring and log management.
Define and implement processes and procedures for detecting data breaches. Improve interdepartmental communication and interaction before and during an incident (This is especially true when organisations host the CIPR workshop internally, over 2 days).

Establish and maintain a Computer Security Emergency Response Team to deal with breaches of security policies. Review your PR & communication templates & internal communications approach.
Understand and explain the primary requirement of privacy regulations, like the EU-GDPR, in the context of cyber incident response and cyber resilience. Review and improve the team and organisational structure of IR teams and CSIM (cybersecurity incident management) teams.
Discuss and support the development of innovative methods of protecting information assets, to the benefit of the organisation and the interface between business and information security. Understand areas of improvement of your organisation’s incident response plans. Baselines cyber resilience awareness across the business.
Discuss and support in the development, coordination and evaluation of plans to communicate with internal stakeholders, external stakeholders and the media. Achieve more productive and efficient staff with increased motivation and better learning and career development.
Understand how DORA, NIS2, GDPR and ISO 27001 impact incident response Lower risk of missed reporting deadlines and fines
Confidently lead the first regulated hour of an incident Build and maintain audit-ready evidence, decision logs and clock tracking
Classify incidents and determine reporting obligations Strengthen operational resilience across multiple regulatory frameworks


263c2ff0-85c7-4f90-9980-d5a2cb27030c-1

Continuing Professional Development

  • CPD points can be claimed for this course at the rate of 1 point per hour of training for this NCSC Assured and CIISec-approved course (8 points for one-day public course and 15 points for the two-day internal workshop).
  • (ISC)2 members can claim 8 CPE points after they complete the whole course and obtain the attendance certification.
  • ISACA members can claim 8 CPE points after they complete the whole course and obtain the attendance certification.

43589f1c-3bac-4ec9-af59-44f2fbcc5d3d-1


NCSC-Assured Training in Cyber Incident Planning & Response

Learning Objectives

Here's a quick look at what delegates can look forward to learning in our NCSC Assured Training in Cyber Incident Planning and Response. 

For a more detailed view of the Learning Objectives, you can directly download Complete Learning Objectives PDF.  

Cyber Incident Planning & Response Training

Our NCSC Assured Training in CIPR has been created by one of the world's leading cybersecurity practitioners & a practising global CISO. The CIPR course stands apart for:

  • It's interactive and engaging approach to Cyber Incident Response.
  • The exceptional course content that is enriched with real-world examples and applicability.
  • The compelling bonus materials that ensure continuous learning for attendees even after the training is over. 
  • Providing learners with best practices, operational and tactical strategies, and practical steps to develop a defined and managed approach to cyber incident response. 


Course Content

All the content you need to implement NIST's Computer Security Incident Response Handbook.

All online and public students receive numerous takeaways including immediately usable cyber response checklists, templates like cyber response plans and workflows that you can put to use in your organisation immediately.

This cyber incident response course combines interactive exercises, real-world examples and immediately usable templates. As hands-on cyber incident response training, it gives learners operational and tactical strategies they can apply straight away. 
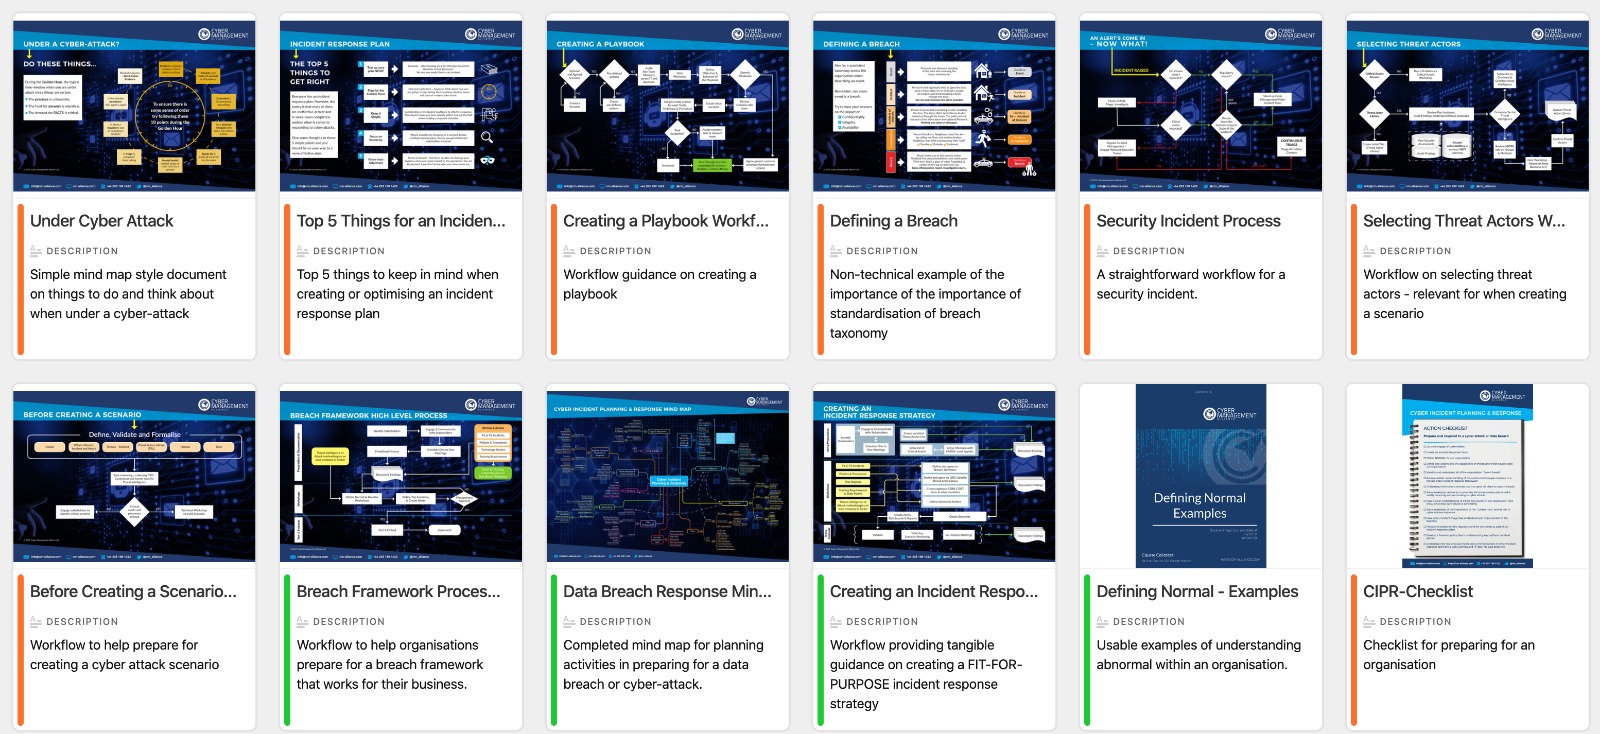
CIPR Documents Image

Cyber Incident Planning & Response Course Modules: DAY 1

  • Interactive Exercises and Collateral
    • Mind Map: Comprehensive exercise on planning for a Cyber-attack
    • Process Workflows: Creating an Incident Response Strategy
    • Process Workflows: Selecting Threat Actors
    • Process Workflows: Creating a Breach Readiness Framework
    • Process Workflows: Responding to an Incident
    • Defending against the Cyber Kill Chain
    • Visibility: Identifying your Crown Jewels
    • Visibility: Identifying Critical Log Data
    • Worksheet: Identifying Privileged Threat Actors
    • Worksheet: Defining & Base-lining 'Normal'
  • Module 1 - Cyber Resiliency

    This module starts by emphasising the importance of asking the question - WHY? Why would an attacker attack your organisation? It delves briefly into the psychology of attacks and builds the foundation for Module 2. In addition, this module introduces the core concept of resiliency in the context of cyber. The module offers:

    • A mind-map that will help you answer this question and also understand what the attacker intends to do with your crown jewels.
    • Explanation of the “whys” with relevant real-world examples.
    • A definition of the ‘Security Fallacy’ and how to work around it.
    • An understanding into why merely denying entry to criminals isn’t enough.

    New for 2026: resilience as NIST now frames it, with incident response as part of governance and risk management, led from the top.

    For full details on this and other modules click here.

  • Module 2 & 2a - Understanding Threat Actors

    Threat actors may sound daunting but fear not. After asking the question, “Why” in the first module, this cyber threat actor section discusses the importance of asking - WHO could damage your critical assets and consequently destroy your business. This section explains the importance of knowing details about your attacker(s) who could target your business. This module offers:

    • An introduction to threat actors, intent and attributes.
    • Threat actors in detail.
    • The TAL or threat actor library and its purpose.
    • Building the Threat Actor Profile.

    New for 2026: AI-enabled attackers, criminals who rent ransomware tools, and fake remote IT workers added to your list of likely attackers.

    For full details on this and other modules click here.

  • Module 3 - Define Normal

    Another key concept in the Cyber Incident Planning & Response course, Define Normal introduces the important idea of baselining or defining an organisational normal and explains its importance in building a cyber resilient business. It goes without saying, unless you can define and understand what’s normal for your digital network, it will be almost impossible to rapidly detect the abnormal. In this module, you will learn:

    • The importance and relevance of this concept, with examples.
    • How to define ‘normal’ for your organisation based on the nature of your business, scale, operational model etc.
    • Applying 'Define Normal' in an organisational context.
    • Understanding and building the organisational baseline.

    New for 2026: knowing what normal looks like now covers cloud apps, user accounts and AI agents (AI tools that take actions on their own), not just networks.

    For full details on this and other modules click here.

  • Module 4 a,b,c & d - The Cyber Kill Chain

    Cyber criminals follow a process and have their own easy-to-follow attack methodology. In this module (also known as the cyber-attack process), we disclose the specific workflows that the majority of advanced and/or smart criminals utilise when they attack organisations and nation-states.

    In these four modules, you will learn:

    • The different phases of attack methodologies.
    • Analysis of the Cyber Kill Chain (Lockheed Martin).
    • The importance of knowing the process flows that can help in the understanding of specific threat models and methodologies.
    • Strategies to counter the Cyber Kill Chain.

    New for 2026: real attacks mapped to MITRE ATT&CK (a public catalogue of attacker techniques), and AI attacks to MITRE ATLAS (its AI equivalent), alongside the Cyber Kill Chain.

    For full details on this and other modules click here.

  • Module 5 - Visibility

    In this module, we introduce an important strategy - the concept that every business must focus on if it wants to increase its breach response and preparedness. The notion that if you stand in a dark room you are blind and oblivious to the surroundings may seem obvious, but this very fact is ignored and overlooked by organisations when planning and strategising on breach-readiness. In this module, students learn:

    • What is visibility and why it's so important as a strategic item in a cyber resiliency strategy.
    • The key and core concepts and terminology to better understand its overall impact on resilience.
    • The importance of log data and its relationship and importance to cyber resilience.
    • The primary requirements for increasing visibility in an organisation.

    New for 2026: which logs you need when the attack is in Microsoft 365, another cloud app or an AI agent, and how long to keep them.

    For full details on this and other modules click here.

  • Module 6 a, b, c & d - The Golden Hour & Incident Management

    The pivotal moment, the ‘golden hour’ and many other important concepts and strategies are discussed in this section.

    • Module 6a deep dives into the ‘golden hour’, its relevance in incident response and its overall importance in the whole incident management lifecycle. This particular module goes deeper into the important aspects of the golden hour, discusses the importance of taxonomy and communications along with introducing and explaining the critical phase of triage and its role in incident response.
    • Module 6b & 6c discuss standards and workflows on incident management introducing several different terms and approaches on optimising existing processes and procedures while maintaining alignment with the various standards and touch on the key benefits of incident response playbooks.
    • Module 6d takes the student through an exhaustive thought process on creating an effective and fit-for-purpose incident response plan with a comprehensive exercise utilising a mind-map based approach.

    New for 2026: rebuilt on NIST SP 800-61 Rev 3. The familiar response steps now link to the six NIST CSF 2.0 functions, and you learn which reporting deadlines start in the first hour.

    For full details on this and other modules click here.

  • Module 7 - Building the Team

    Building a great cybersecurity team also involves walking the tightrope between having a great internal team and liaising with external experts wherever necessary. In this module on Building the Team, students will learn:

    • Identifying the stakeholders, the 'who' and 'what functions' should be included in the core cyber incident management team.
    • Key skills and traits that are essential in members of an effective cyber incident response team.
    • Why contextual experience is more important than technical knowledge when building an incident response team.
    • The importance of encouraging a culture of speaking up in the team, regardless of seniority or experience.

    New for 2026: board and director responsibilities from the UK's Cyber Governance Code of Practice (2025), and who can switch off an AI system.

    For full details on this and other modules click here.

  • Module 8 - Forensics & Investigations

    Forensics and evidence are often overlooked in cyber incident management. Many IT professionals don't have enough experience in handling evidence the right way. Dealing with a cyber-attack requires the ability to ensure chain of custody and ensure the evidence is captured, protected and processed in a way that it can be presented in court without anyone being able to challenge the integrity of that evidence. Delving further into this subject, in this module, we cover:

    • Introduction to forensics principles.
    • Why organisations must sensitise their employees about the regulatory requirement to protect evidence and ensure its forensic integrity.
    • What is a forensics policy, how it can be created and what should its key constituents be?

    New for 2026: evidence from cloud and AI tools, including what people typed into AI tools (prompts), actions taken by AI agents, and audit logs.

    For the full details on this and other modules click here.

  • Module 9 - Regulations & Standards

    The actions that an organisation takes before, during and after an incident can have legal and or financial repercussions. It is imperative, therefore, that the management, IT and Security teams understand the regulations and standards that apply to them and have a well-defined set of policies to cover these regulations. In this module, we cover:

    • The legal, financial or reputational impact that a business can suffer on account of incorrect actions.
    • A look at some common regulations and standards that businesses should be aware of.
    • What is a breach notification and how is it defined in the GDPR?
    • The fines that GDPR stipulates on businesses that are in breach of its regulations.

    New for 2026: a "Which rules apply to you?" exercise that leads into Day 2.

    For full details on this and other modules click here.

  • Module 10 - The Technology Stack

    It goes without saying that technology plays an extremely crucial role in all aspects of cyber incident response and management. The challenge is that most organisations have a messy and complex technology stack. A huge part of the objective of cyber incident planning and response is to evaluate your technology stack and ensure that it is optimised and ready for a cyber-attack. In this module, students will learn:

    • The common mistakes organisations make while buying technology and building a technology stack.
    • The problems a disorganised and incoherent technology stack can create for the business in case of an incident.
    • Understanding the technologies that underpin an effective breach-ready organisation.
    • Analysis of core technology requirements.

    New for 2026: where AI genuinely helps detection and response, and where it adds risk.

    For full details on this and other modules click here.

  • Module 11: Communications & PR in Incident Management

    This module focuses on the communications challenges that arise during cyber incidents and crises. It examines internal stakeholder communications, customer and supplier notifications, regulatory communications and media engagement. The module highlights the importance of:

    • Delivering timely, accurate and transparent communications
    • Crisis communications that support effective incident management
    • Maintaining stakeholder trust during a crisis
    • Protecting organisational reputation during and after a cyber incident

    New for 2026: deepfakes in a crisis, verifying statements, and communicating when email and Microsoft Teams are compromised.

Cyber Incident Planning & Response Course Modules: DAY 2

  • Module 12 - AI Incident Response: Deepfakes, Hijacked AI Agents and Attacks on Your AI

    Govern · Detect · Respond · Recover | NIST SP 800-61 Rev 3 · UK GDPR · OWASP Top 10 for LLM Applications · OWASP Top 10 for Agentic Applications

    Your finance team's AI assistant has just changed a supplier's bank details after reading an email with hidden instructions planted by an attacker. Ten minutes later, the "CFO" calls on video to approve the payment.

    Can you answer these?

    1. Who in your organisation has the authority to switch off an AI agent, and what stops when you do?
    2. Is this a personal data breach, and which regulator's reporting deadline is already running?
    3. Are your AI tools' prompts and actions being logged, and for how long?

    AI has changed both sides of incident response. Attackers use it to impersonate executives and to turn your own AI tools against you. In this module you learn to spot AI-driven incidents, make the decisions only managers can make, and report incidents correctly.

    You will practise:

    • Spot the fake: stop a deepfake payment request by checking through a separate, trusted channel. You leave with a payment verification checklist.
    • Is it an incident? Classify six AI scenarios and name the owner and reporting deadline for each. You leave with an AI incident classification guide.
    • Follow the hidden instruction: trace how a hidden instruction in an email makes an AI assistant leak data, and where a safeguard stops it. You leave with a one-page AI attack path diagram.
    • Kill switch: list your AI tools and decide who can disable each one. You leave with a list of your AI tools and a plan for switching each one off.
    • Live exercise: run an AI incident from first alert to a draft regulator notification.

    Built on real cases, including the 2024 deepfake video call that cost Arup about US$25m.

  • Module 13 - Ransomware Incident Response: Extortion, Recovery and Executive Decisions

    Govern · Respond · Recover | NIST SP 800-61 Rev 3 · UK sanctions rules · UK ransomware payment proposals · DORA · NIS2 · UK GDPR

    It is Saturday morning. Production has stopped, backups are encrypted, and the attackers' leak website is counting down from 72 hours with your customer data as the prize. Your insurer wants to know if you will pay.

    Can you answer these?

    1. Who decides whether to pay, and what must be checked before anyone negotiates?
    2. Which systems come back first, and how long can the business survive without each one?
    3. If the attacker contacts your customers directly, what do you say, and when?

    At M&S, the 2025 attack meant weeks without online sales and an expected £300m hit to profit. This module puts you in the room for the decisions boards actually face: pay or not, how to handle data-theft extortion, and how to restore the business in the right order. It covers UK sanctions rules and the government's ransomware proposals, so your decisions stand up afterwards.

    You will practise:

    • Pay or not? Work through sanctions checks, insurer, legal and law enforcement steps, and defend your decision. You leave with a ransom decision framework.
    • Leak-site countdown: respond when attackers start contacting your customers. You leave with an extortion communications plan.
    • Restore order: set the recovery sequence for ten systems that depend on each other. You leave with a recovery priority list.
    • Live exercise: lead a weekend ransomware incident from detection to recovery and reporting.

    Built on real cases, including the 2025 Jaguar Land Rover shutdown and the Kido nurseries extortion.

  • Module 14 - Identity, SaaS and Third-Party Incidents: When the Breach Isn't in Your Network

    Identify · Protect · Detect · Respond | NIST SP 800-61 Rev 3 · DORA · NIS2 · UK GDPR · FCA and PRA third-party rules

    Nobody broke into your network. A caller talked your helpdesk into resetting a password, and a supplier's stolen digital login key (access token) opened your customer database. Your firewall logs are clean.

    Can you answer these?

    1. How does your helpdesk prove a caller is who they say they are?
    2. Which suppliers and apps hold access to your data, and can you cut it off within an hour?
    3. When a critical supplier is breached, who must you notify, and on whose clock?

    Stolen usernames and passwords are now a leading way in, and around 30% of breaches involve a third party (Verizon 2025 Data Breach Investigations Report). This module shows how attackers get in through people, cloud apps and suppliers, and how to respond when the evidence sits in someone else's system.

    You will practise:

    • The helpdesk call: a role-play that tests whether your verification script stops an impersonator. You leave with a helpdesk verification script.
    • Revoke first: decide which access to cut off first when a cloud app is compromised. You leave with an access inventory template.
    • Supplier down: respond when a critical supplier is the incident. You leave with a third-party incident checklist.
    • Live exercise: lead an incident that starts at a cloud software supplier, through to customer and regulator notification.

    Built on real cases, including the 2025 Collins Aerospace outage at European airports and the 2024 breaches of customer accounts at cloud data company Snowflake.

  • Module 15 - Regulated Cyber Incident Response

    This module provides a practical framework for managing regulated cyber incidents across DORA, NIS2, GDPR, ISO/IEC 27001:2022 and the UK Cyber Assessment Framework (CAF). Delegates will learn how to classify incidents, manage regulatory reporting timelines, preserve audit-ready evidence and make defensible decisions when facts are incomplete. The module also explores how auditors, regulators and senior leaders evaluate incident response activities, helping organisations demonstrate compliance, operational resilience and accountability during and after a cyber incident.

    It covers:

    • Regulated Incident Decision-Making
    • DORA Incident Reporting & ICT Resilience
    • NIS2 Significant Incident Management
    • UK Cyber Assessment Framework (CAF)
    • ISO/IEC 27001 Incident Management & Audit Evidence
    • GDPR Personal Data Breach Response
    • Multi-Regime Incident Response Exercise
    • UK NIS Regulations 2018 and the Cyber Security and Resilience Bill (proposed)
    • FCA and PRA operational incident reporting (rules apply from 18 March 2027)
    • Swiss reporting duties: BACS (24 hours), FINMA and the FDPIC
    • One-page comparison of reporting deadlines across the UK, EU and Switzerland
  • Module 15a: DORA Incident Response Requirements

    This module focuses on the Digital Operational Resilience Act (DORA) and its impact on incident management within financial services and supporting organisations.

    Key topics include:

    • DORA applicability and scope
    • ICT-related incident classification
    • Major ICT-related incident assessment
    • Reporting timelines and notification obligations
    • Critical and important function impact analysis
    • Third-party and supplier involvement
    • DORA evidence and audit requirements
    • The major technology suppliers, such as cloud providers, placed under direct EU oversight in November 2025
  • Module 15b: NIS2 Incident Response Requirements

    This module examines incident response obligations under NIS2 and the practical steps organisations must take to identify, assess and report significant incidents.

    Key topics include:

    • Essential and important entity assessments
    • Significant incident determination
    • 24-hour and 72-hour reporting requirements
    • CSIRT and competent authority engagement
    • Cross-border reporting considerations
    • Supplier and third-party coordination
    • NIS2 evidence and governance requirements
    • UK organisations: the NIS Regulations 2018 today, and what the Cyber Security and Resilience Bill proposes (24-hour initial notice, 72-hour full report)
    • EU Cyber Resilience Act reporting for product manufacturers (since 11 September 2026)
  • Module 15c: UK Cyber Assessment Framework (CAF)

    This module explores the UK's Cyber Assessment Framework and how organisations can demonstrate effective response, recovery and operational resilience capabilities.

    Key topics include:

    • CAF v4.0 principles and assessment methodology
    • Response and recovery capability requirements
    • Incident response planning and testing
    • Recovery objectives and restoration testing
    • Post-incident analysis and lessons learned
    • Indicators of Good Practice (IGPs)
    • Preparing for CAF assessments and audits

  • Module 15d: ISO/IEC 27001 Incident Management

    This module focuses on incident management requirements within ISO/IEC 27001:2022 and how organisations can build repeatable, auditable incident response processes.

    Key topics include:

    • ISO/IEC 27001 incident management controls
    • Event, weakness and incident classification
    • Incident response planning and preparation
    • Evidence preservation and chain of custody
    • Design and operating effectiveness
    • Post-incident reviews and continual improvement
    • Audit-ready incident documentation

  • Module 15e: GDPR Incident Response Requirements

    This module examines personal data breach obligations under UK GDPR and EU GDPR, helping organisations understand when, how and why breach notifications may be required.

    Key topics include:

    • Personal data breach identification
    • Controller and processor responsibilities
    • Risk and high-risk assessments
    • Supervisory authority notifications
    • Data subject notification requirements
    • UK GDPR and EU GDPR considerations
    • Breach records and accountability requirements
    • Changes under the UK Data (Use and Access) Act 2025
  • Module 15f: Real Incidents through Regulatory Lenses

    Nine real incidents from CMA's Cyber Insights briefings, examined through DORA, NIS2, GDPR, CAF and ISO/IEC 27001. For each one: what was triggered, which reporting deadlines started and what the evidence needed to show.

    Key topics include:

    • Deep dives: the AWS cloud outage, the European airports outage (Collins Aerospace), Western Isles Council, Jaguar Land Rover and Kido nurseries
    • Quick-fire cases: the London boroughs cyber attack, the F5 breach, the Shai-Hulud software supply-chain attack and the Asahi brewery ransomware attack
    • Classification, notification decisions and reporting deadlines in each case
    • What good evidence would have looked like
  • Module 15g: Multi-Regulatory Exercise

    This capstone module brings together DORA, NIS2, GDPR and ISO/IEC 27001 through one realistic cyber incident involving a financial services firm, a cloud MSP, cross-border services and potential supply chain impact.

    Key topics include:

    • Managing one incident across multiple regulatory regimes
    • Suspicious privileged access and authentication compromise
    • Cross-border customer authentication outage
    • DORA, NIS2, GDPR and contractual notification triggers
    • Regulatory clock tracking and executive escalation
    • Media pressure, customer communications and legal review
    • Audit-ready evidence, decision logs and corrective actions

Past CIPR delegates: upgrade to CIPR-AI

Your CIPR foundations still apply. Here is what has changed since you trained: NIST has rewritten its incident response guidance (2025), new reporting deadlines have arrived or are on the way (DORA, NIS2, the EU Cyber Resilience Act, and FCA and PRA rules from 18 March 2027), and attackers have started using AI.

Join Day 2 only

As an existing client or past CIPR delegate, you can purchase Day 2 only to attend all three new modules without repeating Day 1. Day 2 opens with:

  1. AI Incident Response
  2. Ransomware Incident Response
  3. Identity, SaaS and Third-Party Incidents

These are followed by Regulated Incident Response, reporting deadlines across the UK, EU and Switzerland, and real-incident case studies. The upgrade is a full Day 2 booking; there is no half-day option.

What you take back to work: a payment verification checklist, an AI incident classification guide, a plan for switching off each AI tool, a ransom decision framework, a recovery priority list and a third-party incident checklist.

You receive a CMA certificate of attendance. Your CIPR certificate records the NCSC Assured course you completed; the 2026 modules and updates are CMA additions and are not examined.

Update your plans before the FCA and PRA incident reporting rules apply on 18 March 2027. Upgrades run live in the virtual classroom or in-house for your team.


STUDENT FEEDBACK & TESTIMONIALS

Cyber Incident Response Course - Testimonials

Check out the 1000+ Written and Video Testimonials about our Cyber Incident Planning & Response course from attendees.

Our course participants come from companies including Microsoft, Adobe, UK Police Cyber Crime Teams, Banks including UBS, Swiss National Bank, RAKBANK, Swiss-CERT and more.
Wayne Parks
A really good session. The trainer is really knowledgeable and presented the course in a really understandable format that the participants really enjoyed.
Wayne Parks
Head of ICT Warwickshire Police
Catherine Gloor
It was really spot on, very practical, non-technical. I have a couple of great take aways for my every day work. Highly recommend it for non-technical people.
Catherine Gloor
Director Group Information Security UBS
Suraj Singh
It was amazing. Amar is not just a trainer, he’s an industry expert, and from his experience and knowledge, I actually got some amazing insights.
Suraj Singh
Head of SOC Microsoft
Euan Ramsay
I found today’s course very productive - discussing the various aspects of incident response. The course is very clearly presented; I fully understood the content and look forward to putting some of the stuff into practice. Thank you.
Euan Ramsay
CSIRT Director, UBS
Cyber Incident Response Team
Brilliant course with lots of good examples. A course to recommend to any incident response team.
Cyber Incident Response Team
Swiss National Bank
Sapan Talwar
I feel the day was really well spent in terms of understanding and getting newer or additional knowledge around this concept and the trainer was absolutely wonderful in sharing and articulating this.
Sapan Talwar
Head of Information Security - Adobe
Robin Smith
I have been attending CMA’s Cyber workshop and we’ve been reviewing incident response. They’ve been directing us towards good cybersecurity practices; they’ve been reviewing our current ideas, and they’ve been adding real value to our Cyber Security response. I thoroughly recommend using CMA for the future.
Robin Smith
Head of Cyber Security - South Yorkshire NHS
Vanessa Smith
I have attended the CIPR training course and I have to say I was very impressed with the course and its content. You don’t need to have IT skills or an insight into IT. But what it does do is, in layman terms, sets out the key issues.  This course is very good.
Vanessa Smith
DCI, Head of Cyber Crime Unit, West Yorkshire Police
KS Ramakrishnan
I wish all Senior Executives attend this course. It’s the most practical course I have ever attended. It teaches you not just how to understand but also how to respond to a Cyber Attack.
KS Ramakrishnan
CRO, RAKBank, UAE
Sanjay Khanna
I found the course to be very interesting. It's not the usual bookish theoretical type of course. It was quite interactive.
Sanjay Khanna
CIO, Rakbank

About the NCSC - National Cyber Security Centre
NCSC Certified Training ColourLaunched in October 2016, the NCSC or National Cyber Security Centre is headquartered in London and brings together expertise from CESG (the information assurance arm of GCHQ), the Centre for Cyber Assessment, CERT-UK, and the Centre for Protection of National Infrastructure.

The NCSC Assured training is designed to assure high-quality training courses delivered by experienced training providers. The courses are assessed at two levels, namely, awareness and application.
apmg-international-logo-stacked-1This course has been certified for the application level of incident response in the areas of Risk Assessment, Business Continuity Planning and Incident Management. The Application level is for anyone looking for in-depth courses for their professional development.
CIIS-Logo_full_colou_tiny

The Chartered Institute of Information Security (CIISec) is the only pure-play information security institution to have been granted Royal Charter status and is dedicated to raising the standard of professionalism in information security. CIISec represents professionalism, integrity and excellence within the information and cybersecurity sector.

The NCSC Assured Training and the Chartered Institute of Information Security's (CIISec) accreditation enables organisations to distinguish between reputable courses and ones that have not been validated using a Government-endorsed assessment process.

Optional Online Examination

Following the completion of the training course (Public, Internal, Instructor-led or Self Paced Learning) all students have the option of earning a cyber incident response certification by successfully passing the APMG International examination of the NCSC Assured Cyber Incident Planning and Response Training. The exam is administered by APMG International and invigilated by ProctorU who provide secure live and automated online proctoring services for academic institutions and professional organisations. 

Number of Questions: 30
Passing Score: 50%
Exam Duration: 25 Mins
Exam Format: Multiple Choice
Exam Delivery: APMG Exam Portal and ProctorU
 

NCSC CIPR Digital BadgeOur digital badges are issued by youracclaim.com, the world's most trusted digital credential network for professional associations and corporate learning. The badges are secure, digital representations of your professional development credentials (certification in incident response). Embed your digital badge on an email signature, website, social media profile or a digital CV.

Earning this incident response certification demonstrates verified, real-world response skills to employers and clients.

Students who have passed the exams and earned an incident response certification have come from organisations including Microsoft, Adobe, NHS, numerous Government departments and Police forces, Unilever, IBM, CISCO, Ernst and Young, Deloitte, KPMG, UBS, RBS, Barclays, Goldman Sachs, Bank of America, TATA Consultancy Services and many many more. 

 

Cyber Incident Planning & Response Brochure Download

Meet the Trainer 

Amar Singh has a long history and experience in data privacy and information security. Amar has served as CISO for various companies, including News International (now News UK), SABMiller, Gala Coral, Euromoney and Elsevier. Amongst various other activities, Amar is a Global Chief Information Security Officer and Trusted Advisor to a number of organisations including a FTSE100 firm, and is chair of the ISACA UK Security Advisory Group. He also founded the not-for-profit cybersecurity service for charities, Give01Day.

Amar_Singh_CISO (1).jpg

Amar has the highest integrity and is trusted by FTSE100 companies with some of the most sensitive commercial information. He has been involved with highly sensitive forensic investigations.

He has the ability to deal with both technically-astute, board-level executives and lead an organisation's information security direction. Apart from his experience and abilities, Amar holds a number of industry-recognised certifications, such as ISO 27001 Certified ISMS Lead Implementer, MoR, CRISC and CISSP certification.

Amar is an industry-acknowledged expert and public speaker and is regularly invited to speak and share his insights by some of the largest and most respected organisations in the world including The BBC, The Economist’s Intelligence Unit, The Financial Times, SC Magazine, InfoSec Magazine, Computer Weekly, The Register and the AlJazeera English Channel.
Amar_Media_Logos.jpg

Why not book a discovery call to discuss your requirements?

Want more information on the NCSC Assured Training in Cyber Incident Planning and Response? Book a no-obligation discovery call with one of our consultants. 

Let us show you why our clients trust us and love working with us.

All trademarks, service marks, trade names, product names, service names and logos appearing on the site, or on printed or digital material are the property of their respective owners, including in Cyber Management Alliance Ltd. Any rights not expressly granted herein are reserved.

The APMG International and swirl device logo is a trade mark of the APM Group Limited, used under permission of The APM Group Limited. All rights reserved.

Frequently Asked Questions

  • What is CIPR-AI incident response training?

    CIPR-AI is the 2026 edition of our NCSC Assured Cyber Incident Planning & Response course. Every module has been updated for 2026, the course is aligned to NIST SP 800-61 Rev 3 and the NIST Cybersecurity Framework 2.0, and there are three new modules: AI Incident Response; Ransomware Incident Response; Identity, SaaS and Third-Party Incidents. Every new topic is taught through interactive exercises.

  • Is this an NCSC Assured incident response course?

    Yes. CIPR-AI is built on the NCSC Assured Cyber Incident Planning & Response course, assessed and certified by APMG International under the NCSC Assured Training scheme. Day 1 Modules 1–11 are the NCSC Assured core and are covered by the optional APMG examination. Day 2 (the three new modules and Regulated Incident Response) and the 2026 modules and updates are CMA additions and are not examined.

  • Does this course include AI incident response training?

    Yes. The AI Incident Response module covers deepfake fraud, attacks on the AI tools you use and hijacked AI agents, and the reporting that follows: UK GDPR personal data breaches, sector rules such as NIS2 and DORA, and the EU AI Act where it applies to you. Most organisations use AI rather than build it. Under the EU AI Act, the companies that build high-risk AI systems must report serious incidents; organisations that use them must tell the provider and the authorities. After the EU's 2026 changes to the AI Act, these duties apply from 2 December 2027 for most systems. You practise the decisions in a live exercise.

  • Does the course cover DORA, NIS2 and UK NIS incident reporting?

    Yes. Day 2 covers DORA, NIS2, UK and EU GDPR, ISO/IEC 27001:2022 and the UK Cyber Assessment Framework, plus the UK NIS Regulations 2018, the FCA and PRA incident reporting rules that apply from 18 March 2027, and Swiss reporting duties to BACS, FINMA and the FDPIC. You practise meeting several reporting deadlines at once on one incident.

  • Does the course cover the UK Cyber Security and Resilience Bill?

    Yes. The Bill is before Parliament and is not yet law. We show what it proposes, including a 24-hour initial notice and a 72-hour full report, against today's NIS rules, so your plans are ready when it becomes law. We will update the content when the final text is published.

  • I took CIPR before. Do I need to retake it?

    No. Existing clients and past CIPR delegates can purchase Day 2 only without repeating Day 1. The first three modules are AI Incident Response, Ransomware Incident Response, and Identity, SaaS and Third-Party Incidents, followed by Regulated Incident Response and case studies. There is no half-day option. See "Past CIPR delegates: upgrade to CIPR-AI" above.

  • What is Cyber Incident Planning and Response Training?

    Cyber Incident Planning and Response Training is a cybersecurity course that teaches organisations how to prepare for, manage and recover from cyberattacks and data breaches. It covers incident response frameworks, threat detection, response procedures and cyber resilience best practices.

  • Who should attend a Cyber Incident Planning and Response course?

    This course is suitable for CISOs, security managers, IT professionals, incident response teams, compliance officers, business leaders and non-technical managers involved in cyber incident management and organisational resilience. No advanced technical knowledge is required.

  • What will I learn in a Cyber Incident Response training course?

    Participants learn how to implement incident response frameworks, identify and manage cyber threats, improve detection and response capabilities, develop response strategies, understand regulatory requirements, and coordinate effective communication during a cyber incident.

  • Does the Cyber Incident Planning and Response course include certification?

    Yes. The course offers an optional examination through APMG International. Upon successful completion, participants can earn a recognised certification demonstrating their knowledge of cyber incident planning and response.

  • How do I book private training for my organisation?

    The CIPR course can be delivered privately for your team, either in-house or as a dedicated virtual class, with scheduling arranged around your organisation’s availability. Private delivery lets you train multiple staff together and tailor the discussion to your own environment and risks. To arrange it, book a discovery call or contact the CM-Alliance team, who will help you confirm dates, format and numbers.

  • How do NCSC-aligned cyber incident response courses improve readiness?

    NCSC Assured training is independently assessed by APMG International, an accreditation body, against the NCSC's standard, so you can be confident it meets a recognised quality benchmark. Courses like CIPR improve readiness by teaching a structured, repeatable approach to incident response — based on the NIST framework — that reduces the time taken to detect and respond to attacks, clarifies roles and decision-making under pressure, and aligns technical and non-technical staff around a common plan before a real incident occurs.

  • What makes cyber incident planning and response training effective?

    Effective training combines a proven framework with real-world application. The CIPR course is built on NIST SP 800-61 Rev 3 and ISO/IEC 27001:2022 objectives, is delivered by a practising Chief Information Security Officer (CISO) with decades of incident response experience, and uses realistic, scenario-based discussion rather than theory alone. Because it has no technical pre-requisites, entire teams — technical and non-technical — can learn together and leave with strategies they can apply immediately.

  • What delivery options are available?

    The CIPR course is available in three formats: self-paced eLearning with immediate online access; scheduled live virtual classroom sessions led by an expert facilitator; and private or in-house delivery for organisations that want to train a group together. An optional examination and certification through APMG International is available with each format.

  • How does this course help with NIST, ISO 27001 and incident response maturity?

    The course teaches you how to apply NIST SP 800-61 Rev 3 and how to meet the objectives of the ISO/IEC 27001:2022 incident management controls (5.24–5.28 and 6.8), mapping recognised international standards to practical, day-to-day incident response. By giving your team a structured approach to preparation, detection, response and recovery, it helps raise your overall incident response maturity and provides evidence that your organisation actively tests and improves its capabilities.

The information on this page and related pages and documents is Copyright of Cyber Management Alliance Ltd. The VCA or Virtual Cyber Assistant term, other terms, information, concepts, ideas, workflows, processes, procedures and other content that directly or indirectly supports the VCA Service are Copyright of Cyber
Management Alliance Ltd. Copyright 2022.

Footer Top Background Image
Simply fill in your details to request a FREE callback 
NCSC Assured Cyber Incident Planning and Response Course