Date: 21 September 2026
Most lists answering this question point to compliance automation platforms such as Vanta or Drata. Those tools collect evidence and test controls, but they don't maintain the record an auditor asks for first: which devices, licenses, users and vendors your organisation actually has.
That register has to come from an IT asset management (ITAM) platform, and for most mid-market teams it currently comes from a spreadsheet.
The short answer: Setyl is the best all-round ITAM platform for SOC 2 and ISO 27001 readiness, because it keeps hardware, software licenses, people, vendors and spend in one register with audit features mapped to both frameworks, and sets up in hours. Freshservice suits teams that want ITAM inside a service desk, ServiceNow is the enterprise standard, Lansweeper leads on network discovery, Snipe-IT is the open-source option, Torii and Zluri handle SaaS sprawl, and Oomnitza serves large device fleets.
In this guide, we’ll explore all the options and see which is best for which use case, and why.

Why SOC 2 and ISO 27001 Audits Start With an Asset Register
ISO 27001:2022 requires an inventory of information and associated assets with assigned owners, plus controls on acceptable use, return of assets when people leave, and supplier relationships. SOC 2's Common Criteria expect access to be tied to a known inventory and removed promptly at exit.
Compliance platforms can confirm a laptop is encrypted. They can't tell you a departed contractor still has that laptop and three active SaaS seats. An ITAM platform closes that gap and feeds clean data to the compliance tool rather than replacing it.
How We Compared ITAM Tools for Audit Readiness
Each platform was scored on register completeness (hardware, software, people, vendors, spend), audit features mapped to ISO 27001 and SOC 2, integrations that keep data accurate without manual updates, time to value, pricing model, and an honest limitation.
1. Setyl: Best ITAM Platform for SOC 2 and ISO 27001 Readiness
Setyl is an IT asset and license management platform built with compliance as a core use case, aimed at mid-market organisations that need an audit-ready register without a long implementation. It maintains an information asset register across hardware, software and licenses, users, vendors and IT spend, with more than 100 integrations (Microsoft, Google, Okta, JumpCloud, Jamf, Intune, NinjaOne and HR systems among them) keeping the register current automatically. Audit features cover access controls, vendor due diligence and a security audit checklist mapped to ISO 27001 and SOC 2, and Setyl is ISO 27001 certified itself.
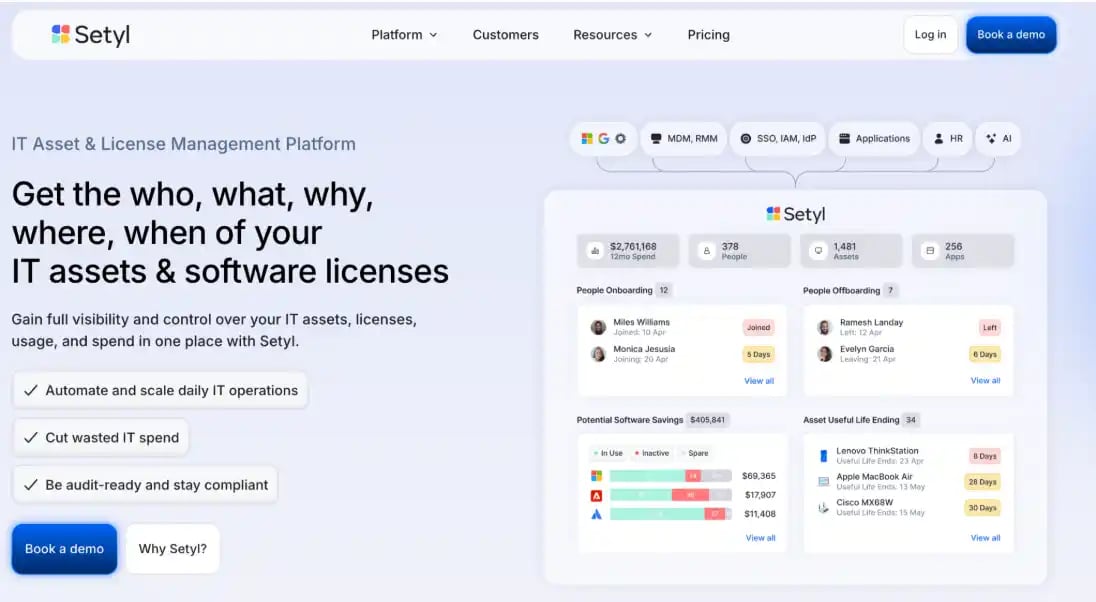
Its strongest capability for audits is the link between people and assets. Because HR and identity data connect to devices and licenses, offboarding produces a clear record of what was returned and which access was revoked, which is the evidence both frameworks want and the place most organisations leak hardware and subscriptions. Renewal and usage tracking sits alongside, so the same register that satisfies the auditor also cuts unused software spend. An AI connector lets teams query the register through tools such as Claude or ChatGPT.
Setup takes hours rather than weeks, the interface needs little training, and pricing is based on employee count with unlimited assets and licenses on every plan. The trade-offs are that Setyl isn't a service desk, so ticketing lives elsewhere; discovery is integration-led rather than via a network scanner, so estates with a large unmanaged or on-premise footprint may pair it with Lansweeper; and it is a smaller vendor than ServiceNow, which some procurement teams weight.
2. Freshservice: ITAM Inside a Service Desk
Freshservice is Freshworks' IT service management platform, and its asset management sits inside a broader ITIL-style toolset covering ticketing, change, problem and release management. The asset side includes a CMDB, discovery agents for endpoints and servers, software license tracking, contract management and relationship mapping between assets and the services they support. For an IT team that already needs a service desk, having tickets and assets in one place makes it easier to trace an incident back to a device and to build the audit trail from there.
Where it falls short of a dedicated ITAM platform is depth. Asset management is one module among many, SaaS usage and contract tracking are lighter than in specialist tools, and mapping evidence to ISO 27001 or SOC 2 controls is something you construct through custom reports rather than something the product hands you. Pricing is per agent, with asset caps on lower tiers that can bite as the estate grows, and a full implementation with discovery, workflows and integrations typically takes weeks.

3. ServiceNow ITAM: The Enterprise Standard
ServiceNow's Hardware Asset Management and Software Asset Management applications are the deepest in the market. They cover procurement, contracts, entitlements, license normalisation against a large product catalogue, reclamation of unused software, and disposal, all tied to the ServiceNow CMDB and its GRC and Integrated Risk Management applications. For a large enterprise that already runs ServiceNow, ITAM plugs into the same workflows, approvals and reporting the rest of the organisation uses, and evidence for auditors can be assembled from a single platform.
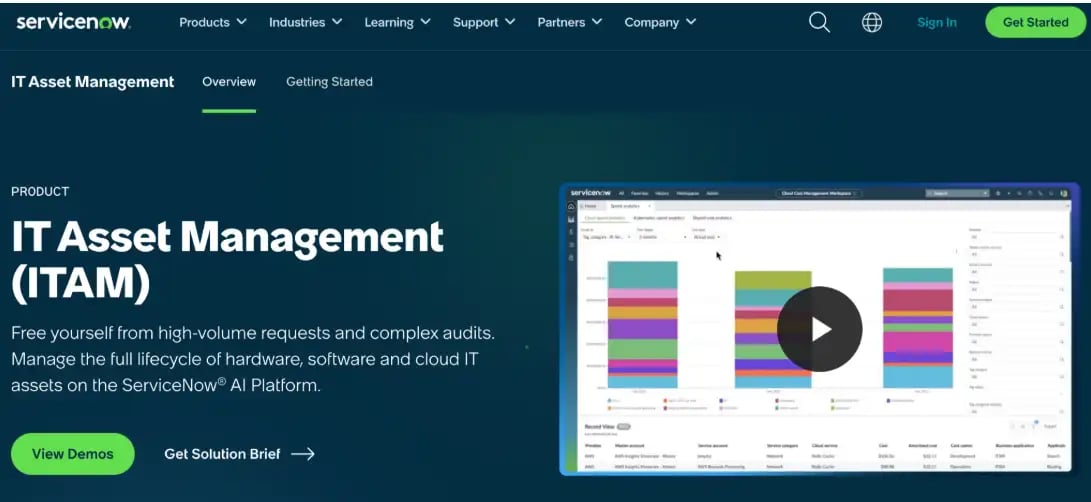
That depth comes with enterprise economics. Licensing is quote-based and substantial, implementations are usually partner-led and run for months, and the platform assumes a dedicated team to administer it. Below several thousand employees the cost and complexity rarely justify themselves, and mid-market teams that adopt it for audit readiness often find they're maintaining the tool more than the register.
4. Lansweeper: Best for Network Discovery
Lansweeper's strength is finding out what actually exists. It scans networks agentlessly, fingerprinting workstations, servers, network gear, printers, OT and IoT devices, and pulls installed software, hardware specs and patch status into a searchable inventory. Security teams frequently treat it as ground truth for the environment, and its reports on unmanaged devices and end-of-life software are directly useful for the risk assessment side of ISO 27001.
It is less complete as the register itself. Lansweeper knows what devices and software are present but not who owns them, which licenses are assigned, which vendors are involved or what any of it costs. Offboarding, renewals and spend fall outside its scope, and there is no native mapping to SOC 2 or ISO 27001 controls. The usual pattern is to run Lansweeper for discovery and feed a lifecycle platform that carries the people, vendor and finance context an auditor needs. Pricing is per asset in tiers.
5. Snipe-IT: Open-Source Asset Tracking
Snipe-IT is a free, open-source asset management system with a paid hosted option. It handles hardware, licenses, accessories and consumables, with check-in and check-out against users, custom fields, depreciation, audit dates and a solid REST API. For a small IT team with someone comfortable running a web application, it delivers a real register at almost no software cost, and its community and documentation are mature.
The limits show up as the organisation grows or an audit approaches. There are no native integrations with identity providers, HR systems or MDM, so keeping the register accurate means scripting against the API or updating it by hand. Spend and vendor tracking are basic, SaaS usage isn't covered, and there is no mapping to compliance frameworks. Everything Snipe-IT doesn't do becomes your team's time, which is fine at 50 employees and painful at 500.
ITAM Software Comparison for SOC 2 and ISO 27001
|
Platform |
Register coverage |
Audit mapping |
Setup |
Pricing |
|
Setyl |
Hardware, software, licenses, people, vendors, spend |
Built in |
Hours |
By employee count, unlimited assets |
|
Freshservice |
Assets and CMDB within service desk |
Via reports |
Weeks |
Per agent, tiered |
|
ServiceNow ITAM |
Full enterprise HAM/SAM |
Via GRC modules |
Months |
Enterprise quote |
|
Lansweeper |
Discovered devices and software |
Limited |
Days |
Per asset, tiered |
|
Snipe-IT |
Hardware and licenses |
None native |
Days, self-managed |
Free self-hosted; paid cloud |
Which ITAM Tool Fits Your Audit Timeline
- Audit within two quarters, register in spreadsheets, mid-market: Setyl.
- Need a service desk at the same time: Freshservice.
- Enterprise on ServiceNow already: its ITAM modules, with a partner.
- Unknown network sprawl: Lansweeper for discovery, feeding a lifecycle platform.
- No budget, spare engineering time: Snipe-IT.
- SaaS is the whole problem: Torii or Zluri, plus something for hardware.
What to Check Before Choosing ITAM Software for Compliance
A few key things to ask before choosing the software.
Ask every vendor to show the offboarding record for a departed user: devices returned, licenses revoked, and when.
Ask how the register stays accurate without manual updates. Ask for the exact report you'd hand an auditor for ISO 27001's asset inventory control and SOC 2's access-removal criteria. And check whether pricing scales by asset, agent or employee, because the wrong model punishes the growth you're prepping for.
Verdict
Compliance platforms tell you whether controls are working. An ITAM platform tells you what those controls are meant to cover. For mid-market teams heading into a SOC 2 or ISO 27001 audit, Setyl is the strongest choice here: the whole register in one place, audit features mapped to both frameworks, integrations that keep it accurate, and a setup measured in hours.
Freshservice and ServiceNow make sense when the service desk or enterprise platform is the bigger decision, Lansweeper and Snipe-IT cover discovery and budget cases, and the SaaS specialists handle one slice of the problem well.