Date: 17 September 2026
Most security policies say something confident about email. They mandate encryption in transit, specify retention periods, name the approved client and warn staff about attachments from unknown senders. The document reads well, so it gets signed off, filed, and produced during audits.
Then someone checks what actually happens. A director forwards board papers to a personal account so she can read them on the train. A supplier sends an invoice to a shared inbox that nine people can open. A contractor works from their own domain, because onboarding them properly would have taken three weeks.
The policy and the practice have drifted apart, and nobody noticed because nothing had gone wrong. And then something does go wrong, and that policy-practice drift is where a surprising number of incidents begin.

What the policy assumes about email
Written policy describes a single, controlled channel. Everything flows through the corporate tenant, everything is logged, and everything is recoverable. It's a tidy picture but it's rarely accurate.
The Cyber Security Breaches Survey 2025 found phishing remains by far the most common attack type reported by UK businesses. That figure gets quoted in board packs constantly. What gets quoted far less often is the follow-on question: if phishing is the dominant route in, how confident are you about every route your organisation's messages actually travel?
Where the document and the desk diverge
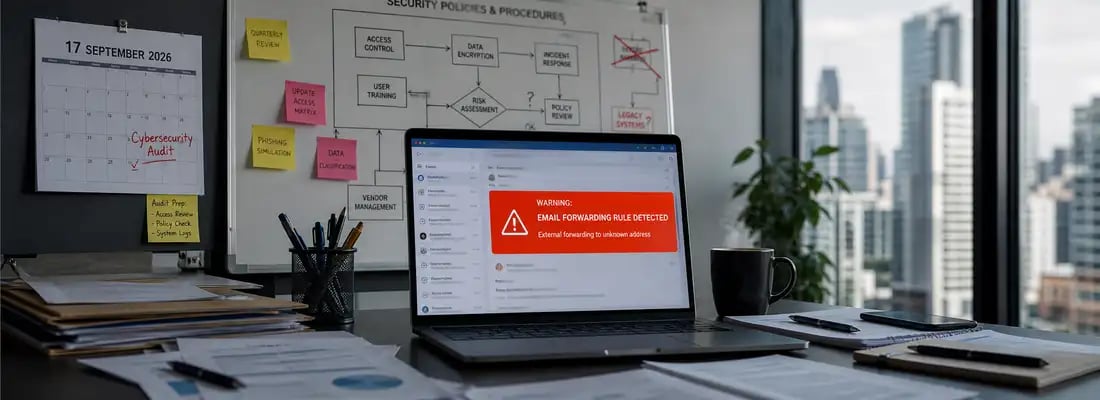
The drift is usually mundane. Someone sets up an auto-forward during annual leave and never removes it, or a team creates a shared mailbox for convenience and shares one password between them.
Neither of those are malicious — and that is rather the point. Our guide to recognising cyber crime and social engineering covers how attackers exploit exactly this kind of ordinary, well-intentioned shortcut. An attacker does not need a zero-day when a forwarding rule will do the job.
Testing your assumptions before an incident does
Treat this as an evidence exercise rather than a questionnaire. Pull the list of active forwarding rules across your domain and see whether you can explain every one of them. Check which mailboxes are shared, and who still has access after leaving. Ask whether your provider's default settings match what your policy claims, because plenty of organisations discover their email is quietly doing something the document never anticipated.
Then run the same check on the accounts sitting outside the tenant. Board members, non-executive directors and long-term contractors frequently operate from personal addresses, and they handle some of the most sensitive material you produce.

Matching the Policy to Reality
You have two options when policy and practice diverge, and only one of them is honest. Either bring the practice up to the document, or rewrite the document to describe what you can genuinely enforce. Organisations that pick the second option often end up with a shorter, blunter policy that people actually follow.
The version nobody should choose is leaving the gap open and hoping the auditor does not look too closely. Assessors increasingly do look, and so do attackers. A policy describing an email estate you do not have will read, after an incident, as a record of what you meant to do.